- GDPR compliant
- ISO 27001 & 9001
- Verified Microsoft Partner
Maximum security through certified standards
Privacy and security at MyTaag
MyTaag stores and processes all data in Hetzner Online GmbH data centers in Nuremberg, Germany, works in line with the GDPR under a data processing agreement and protects accounts with two-factor authentication and permissions per area.
Protecting information is paramount when using digital business cards. MyTaag meets the strictest security requirements for companies and authorities to ensure legally secure and technically flawless data exchange.
- Made in Germany
- Servers in Germany
- Compliant with EU regulations
- Verified Microsoft Partner
- As seen on the German version of Shark Tank
At a glance
Infrastructure & hosting
Servers at Hetzner in Nuremberg, encrypted transmission via SSL/TLS. More on hosting
Data processing
Standardized DPA for corporate customers, privacy by design and by default. More on data processing
Consent for leads
Consent right in the form, with optional double opt-in. More on consent
Access control
2FA by email code, permissions per area, secure sessions. More on access control
Certifications
Certified to ISO 27001 (information security) and ISO 9001 (quality management) by DICIS. More on certifications
Deletion, export, offboarding
Export leads, remove users cleanly. More on deletion and export
Infrastructure & hosting in Germany
Sovereignty through German server location. The entire system architecture is designed for maximum security and reliability. MyTaag is developed and operated in Germany.
- Server location Nuremberg: Data is stored and processed in Hetzner Online GmbH data centers in Nuremberg, Germany.
- Legal security: Due to hosting in Germany, the entire platform is subject to the world's strictest data protection laws.
- Encrypted transmission: Data transfer takes place via state-of-the-art SSL/TLS encryption protocols to ensure protection against unauthorized access during transmission.
Data processing agreement and GDPR compliance
Data protection as a systemic standard. MyTaag was developed according to the principles of “Privacy by Design” and “Privacy by Default”.
- Full GDPR compliance: All functions of the digital business card are strictly aligned with the requirements of the European General Data Protection Regulation.
- Data processing agreement (DPA): Standardized contracts for data processing under Art. 28 GDPR are available for corporate customers and meet the compliance requirements of modern companies.
- Questions from your data protection team: We're happy to go through technical and organizational measures or the service providers involved with you directly – by email at hello@mytaag.com or in a demo.
How we process personal data on our website is described in our privacy policy.
Lead capture
Consent for lead capture
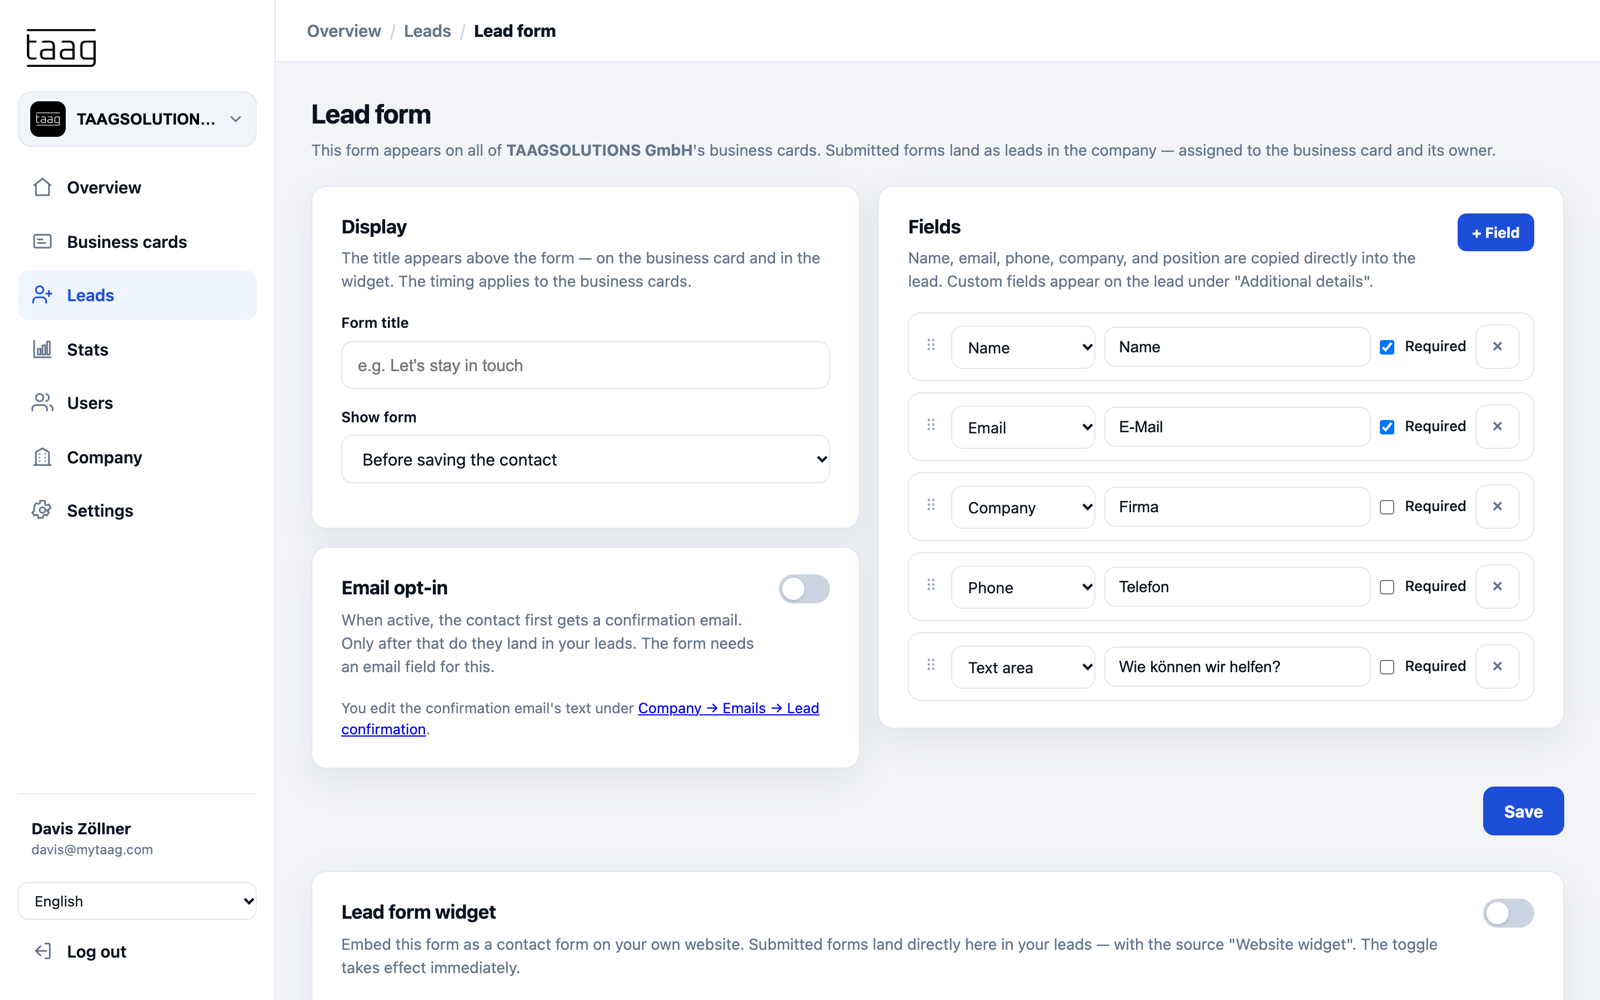
Legally secure lead capture: The integrated forms for data collection are configured by default to ensure legally secure collection of consents (opt-in) directly in the process.
- Consent and privacy noticeThe lead form on the business card and the website widget both include consent and a privacy notice.
- Double opt-in by emailIf you like, your contact also confirms consent via a link in an email.
- Only what you needYou decide which fields the form asks for.
Access control
Two-factor authentication, roles and permissions
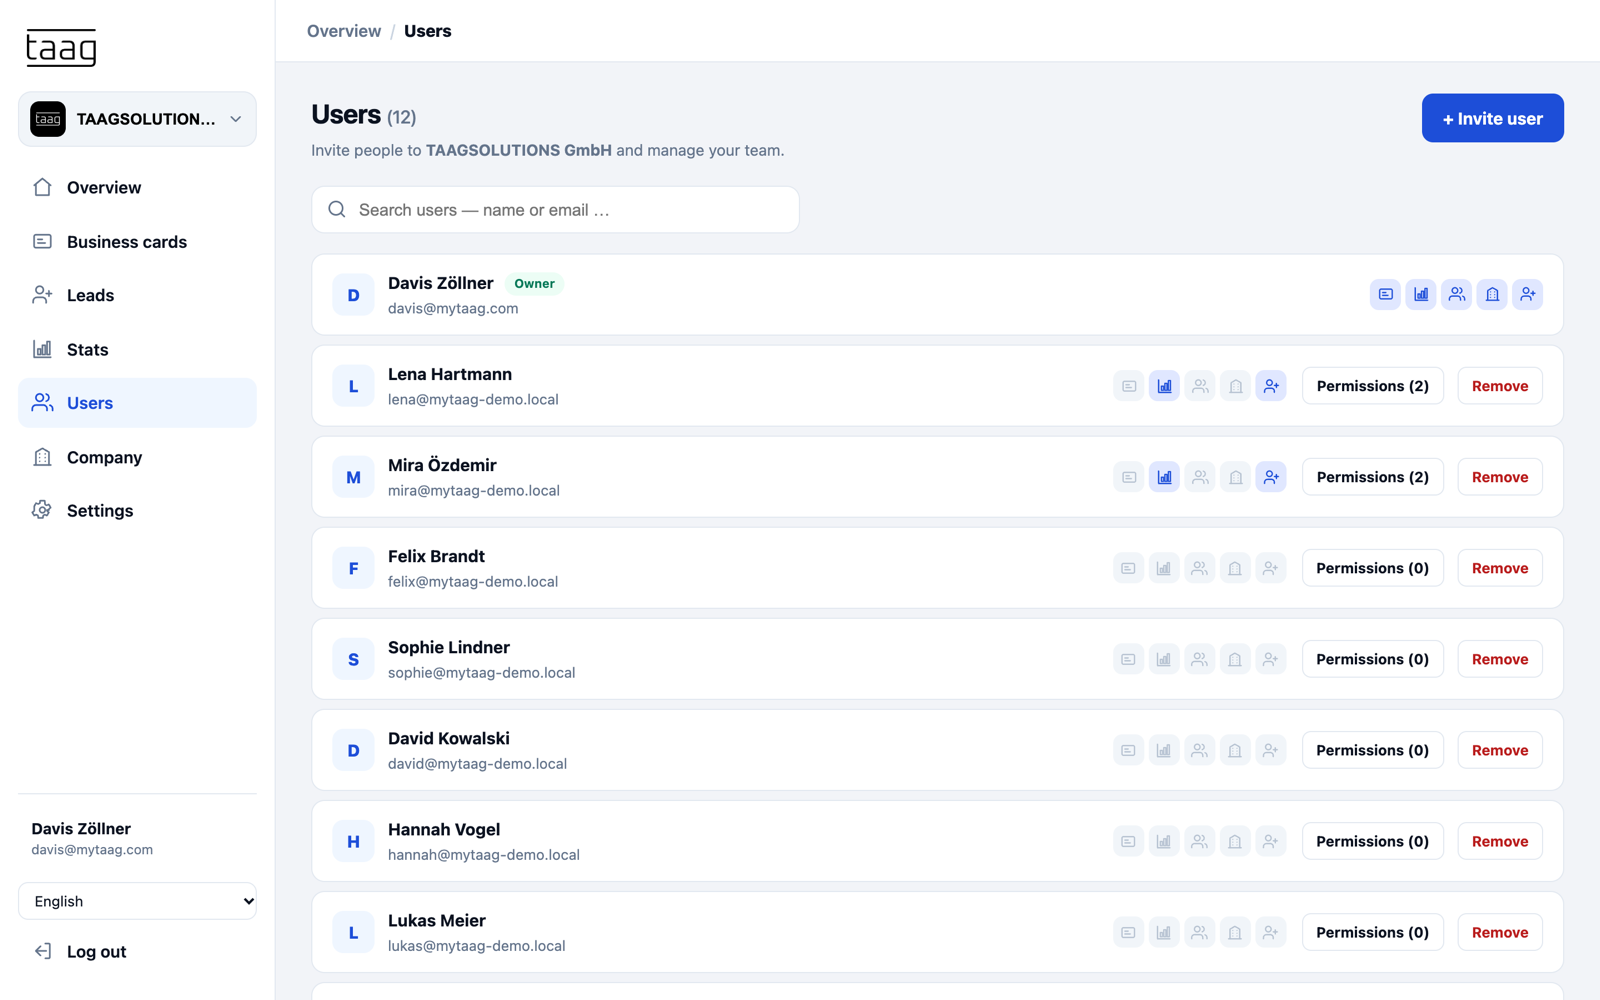
- 2FA by email codeAt sign-in, MyTaag also asks for a code from your inbox. Turning two-factor authentication on or off requires a code, too.
- Permissions per areaBusiness cards, stats, users, company and leads – each person sees and changes only what they're cleared for. Invitations are only possible into your own company.
- Password reset by emailA password can only be changed via a link sent by email. Afterwards, all devices are signed out.
- Secure sessionsSign-in sessions are encrypted and stored on the server only as a hash.
Enterprise security features
Central control and technical accessibility. The architecture enables secure integration into existing corporate structures without creating additional risks.
- Central profile management: Content and access permissions are controlled via an administration dashboard. In the event of personnel changes, profiles can be deactivated or updated in real time.
- No app installation required: Since the application works in the browser, security risks from third-party software on mobile devices (Bring Your Own Device) are eliminated.
- Hardware security: The NFC chips used in the physical cards only serve as an encrypted link to the digital profile and do not store any sensitive personal data themselves.
Certifications
Tested quality according to global standards. MyTaag is certified to ISO 27001 and ISO 9001 by the certification body DICIS; compliance is audited regularly.
- ISO 27001 (information security): The platform is operated according to the world's leading standard for information security management systems. This ensures the confidentiality, integrity and availability of information.
- ISO 9001 (quality management): This certification guarantees optimized internal processes and continuous quality control in product development and operations.
Deletion, export and offboarding
Your data belongs to you. That's why you can take it with you and remove it cleanly at any time.
- Export: Export leads as CSV or Excel at any time – for your CRM or your own records.
- Offboarding: When someone leaves the company, you remove them from MyTaag. You choose whether their business cards or devices are kept – for example to reassign them – or not.
- Unlink NFC cards: An NFC card can be unlinked from a business card or assigned to someone else at any time.
- Update profiles instantly: Changes in the dashboard apply immediately, including to the Wallet passes on your team's phones.
FAQ about privacy and security
Where is MyTaag data stored?
In Hetzner Online GmbH data centers in Nuremberg, Germany. Transmission is encrypted via SSL/TLS.
Do I get a data processing agreement?
Yes. Standardized data processing agreements (DPA) under Art. 28 GDPR are available for corporate customers.
Is lead capture GDPR compliant?
Yes. The lead form and the website widget collect consent directly in the process, with optional double opt-in by email.
How are accounts protected?
With two-factor authentication by email code, permissions per area, password changes only via an email link followed by sign-out on all devices, and sessions stored only as a hash.
Which certifications does MyTaag have?
MyTaag is certified to ISO 27001 (information security) and ISO 9001 (quality management). The certification body is DICIS; both certificates are audited regularly.
Does the NFC card store personal data?
No. The NFC chip only serves as an encrypted link to the digital profile and does not store any sensitive personal data itself.
What happens to the data when someone leaves the company?
When removing the user, you choose whether business cards or devices are kept. You can export leads beforehand as CSV or Excel.